Welcome to Samsung Security
for Smart TV, Audio and Displays
We believe that the security and privacy protection offered by Samsung Smart TV, Audio
and Displays are paramount to creating some of the world's most trustworthy products and services.
That is why we are always committed to offering steadfast security and
privacy protection in order to provide our customers with the optimal experience.
Security and Privacy
The security and privacy of the customer is considered a top priority.
To achieve this a dedicated team of security experts continues to carry out various security
activities for Samsung Smart TV, Audio, Displays and services.
This site provides important security updates and information related to our products and
services. We always strive to provide an agile and robust, security incident response mechanism.
We investigate all security vulnerabilities affecting Samsung Smart TV, Audio and Displays and services.
And, we provide security updates and information to prevent security risks.
For the protection of Samsung Smart TV, Audio and Displays, we encourage customers to keep their devices
and apps up-to-date.
Rewards Program
Samsung Rewards Program for Smart TV, Audio and Displays is a program to find security vulnerabilities early
on and to compensate bounty hunters for their achievements.
We encourage security experts from all over the world to work with us.
Please check below if you have information about a security issue or vulnerability related to
Samsung Smart TV, Audio and Displays.
Detailed View
TV security team audit
Samsung maintains a dedicated security team to support all samsung TV products as well as their or any
various integrated services such as Bixby.
We, Samsung TV security team, provide security auditing and testing for products, both under development
and released.
We also actively monitor for threats and reports of new security issues.
View more...View less
Internal Security Audit
Samsung TV security team conducts internal security audit as follows.
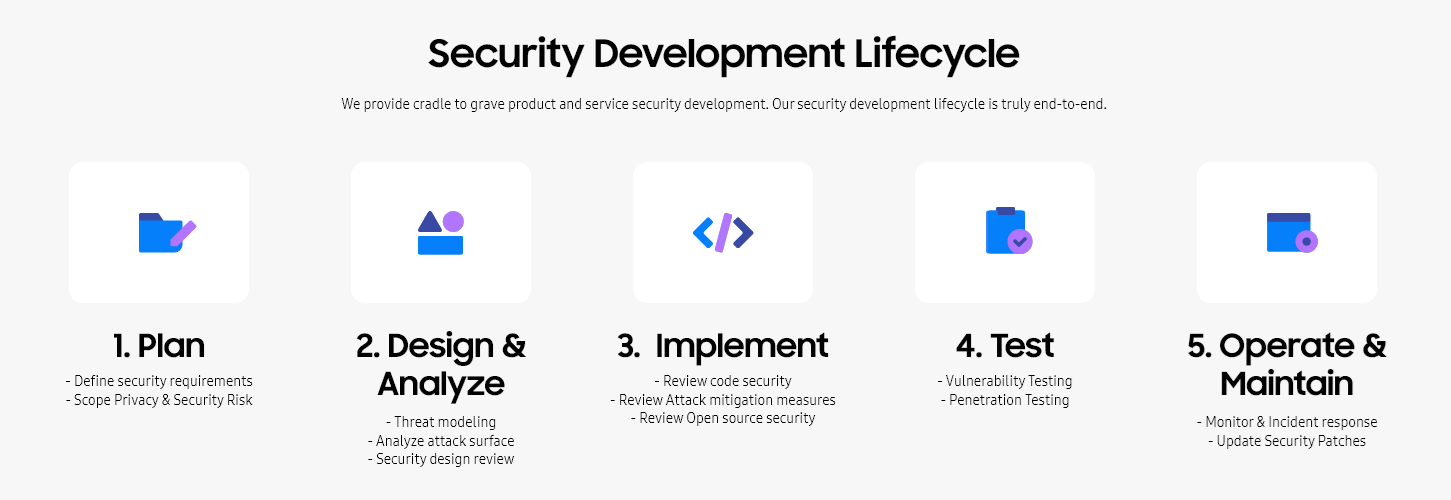
From concept to end of life, Samsung TV security team follows a strict security development process that covers the entire lifespan of Samsung products, services and customer experience.
Samsung security policies extends to classifying, handling and processing how we protect personal data and other forms of confidential data.
Samsung TV security team go through rigorous security design reviews that consider all types of attack vectors.
Samsung TV security team monitor the threat landscape for emerging threats over Samsung devices and services.
Third-party Security Audit
In addition to internal security audits, we also conduct third-party audit. External security experts conduct annual security checks on major products and services. Before and after the release of products and services, we carry out penetration tests to identify additional security vulnerabilities from an attacker's perspective and take immediate action through security patches.
Additionally, through the bug bounty program, we receive reports of security vulnerabilities from hackers worldwide, continuously apply security patches, and strengthen the safety of our products and services.
Considering the test targets and required schedule, black-box testing or gray-box testing is prepared and conducted.
Identified security vulnerabilities are patched within a limited target timeline (max 90 days) to ensure the safety of products and services.
The penetration test is conducted through the following steps.
Planning step: Pre-preparation step for performing security checks. Check the target, takeholder, and determine the scope and rules of security checks. Conduct a series of consultation activities to perform security checks, and define and finalize the roles of each person in charge. Performs lesson learning for the previously performed related projects and determines how to communicate with the client.
Testing step: Actual security check. Information collection, mapping, penetration test, network scanning, vulnerability scanning are performed, and vulnerabilities are derived through this. Obtain authority through derived vulnerabilities or check if additional attacks are possible with related systems around.
Reporting step: Analyze and document vulnerabilities and issues found in the testing step. Write a report on lesson learn related to vulnerabilities, pre-written technical documents, internal/external cases, etc.